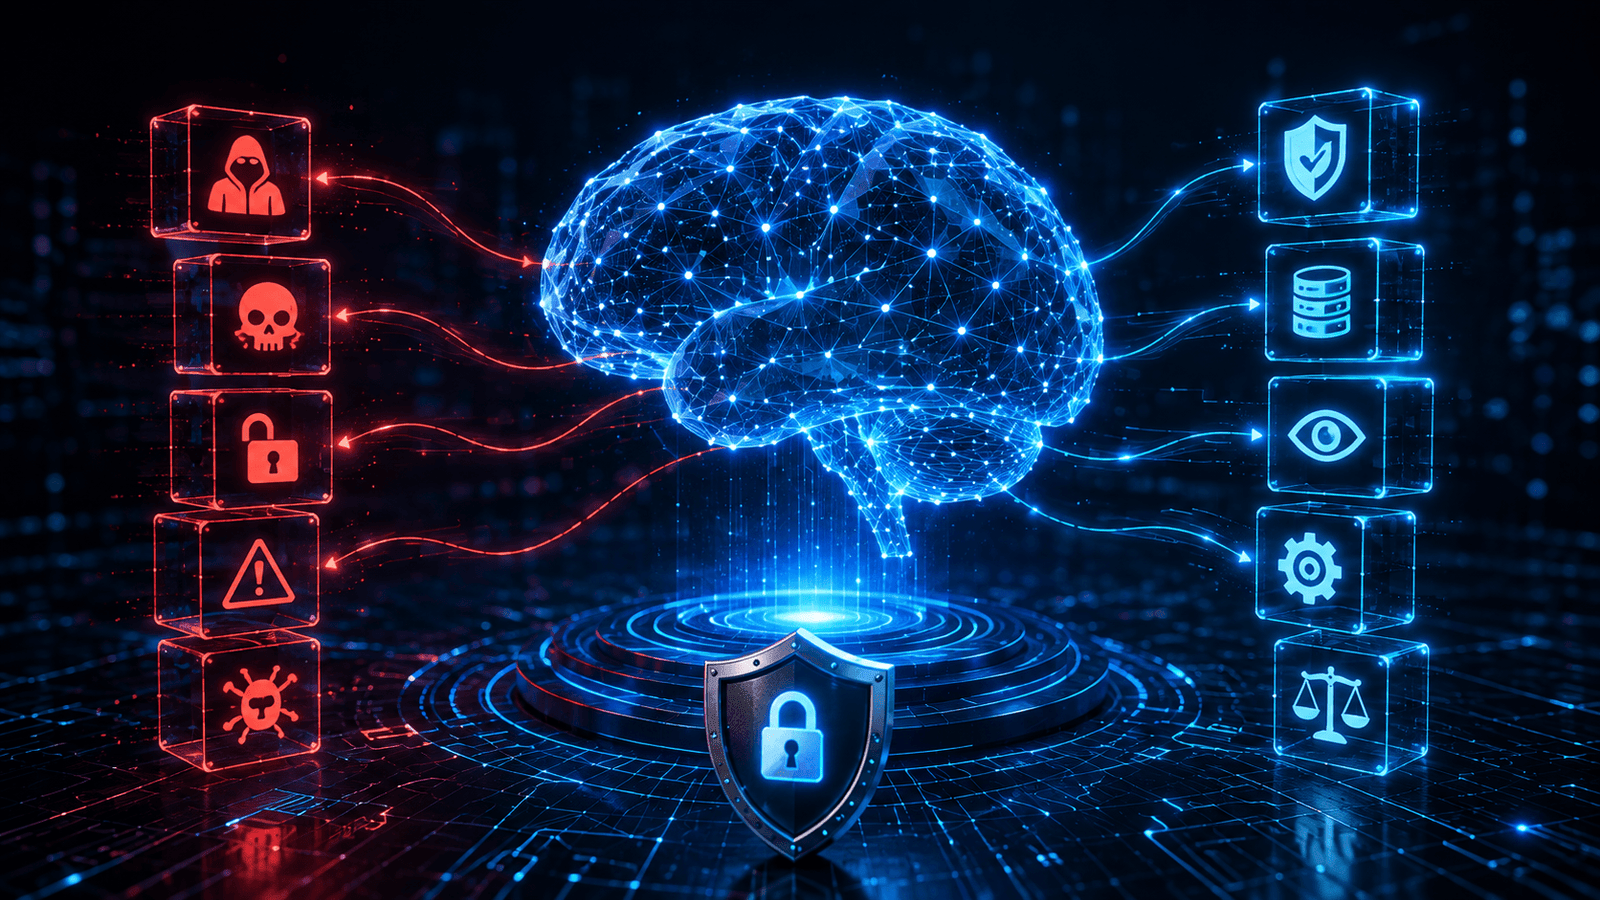
Generative AI security is becoming a broader enterprise cybersecurity problem as companies connect artificial intelligence systems to internal data, software tools, APIs and business processes.
Prompt injection and sensitive-data exposure remain important vulnerabilities, but the security challenge is expanding as AI systems move from generating text and images to retrieving information, calling external tools and taking actions on behalf of users.
That shift is particularly important in 2026. The OWASP GenAI Security Project’s current risk framework covers threats including prompt injection, sensitive-information disclosure, supply-chain vulnerabilities, data and model poisoning, improper output handling and excessive agency. Its review of incidents from the first quarter of 2026 also found security problems increasingly affecting agent identities, orchestration layers and supply chains.
For businesses deploying AI, the lesson is that securing the model alone is no longer enough. Organizations also need to control the data, permissions, software integrations and infrastructure surrounding it.
Prompt Injection Remains a Core AI Security Problem
Prompt injection occurs when instructions supplied directly or indirectly to a large language model alter its intended behavior.
The problem becomes more consequential when an AI system has access to private information or external tools. A manipulated chatbot response may be inconvenient; a manipulated agent with permission to retrieve corporate data or perform actions can create a substantially larger security problem.
OWASP ranks prompt injection first in its 2025 Top 10 for LLM and generative AI applications.
Indirect prompt injection adds another complication. Instructions can potentially be embedded in external content that an AI application processes, rather than being typed directly by its user.
That changes how businesses need to think about trust. Information retrieved by an AI system cannot automatically be treated as safe instructions simply because it came from a document, website or another connected source.
Sensitive Data Can Move Through AI Systems in Unexpected Ways
Enterprise AI applications routinely interact with material that companies would not want exposed publicly, including customer information, financial records, credentials, proprietary documents and internal communications.
OWASP identifies sensitive-information disclosure as another major LLM application risk. Exposure can occur through model outputs or through the broader application handling the model’s data.
The National Institute of Standards and Technology’s Generative AI Profile similarly recommends monitoring AI-generated content for privacy risks and establishing policies governing the collection, retention and protection of data.
Organizations therefore need to consider the entire information path: what users can submit, what the application retrieves, what the model can access, where information is stored and what the system is permitted to return.
Traditional controls such as data classification, access management and monitoring remain relevant, but they have to be applied to AI-specific workflows.
AI Agents Expand the Attack Surface
The emergence of agentic AI makes those controls more important.
Generative AI applications are increasingly able to retrieve information, use APIs and tools, execute code and perform multistep tasks. AI safety testing and sandbox security. A 2026 review published in the Journal of Information and Intelligence described the transition from content generation to agentic action as a new security frontier because greater autonomy can increase the scope of potential harm.
The Center for Internet Security has reached a similar conclusion in its 2026 AI and Large Language Models Companion Guide. CIS notes that systems connected to retrieval tools, memory and external services create risks involving context integrity, tool misuse, data exposure and AI supply chains.
In practical terms, an AI agent should not receive broad permissions simply because automation makes those permissions convenient.
Organizations should apply least-privilege principles to AI just as they would to employees, applications and service accounts. An agent that only needs to read a limited dataset, for example, should not automatically receive permission to modify records or interact with unrelated systems.
The security architecture surrounding an AI agent can become as important as the model itself.
Data Poisoning and Supply Chains Create Different Risks
Not every attack begins with a malicious prompt.
OWASP also identifies data and model poisoning as a major risk. Manipulated information introduced during pretraining, fine-tuning or embedding processes can affect model behavior and the integrity of downstream applications.
AI supply chains add another layer. Enterprise deployments can depend on foundation models, datasets, open-source packages, model repositories, plugins, retrieval infrastructure and third-party services.
That means AI security programs need visibility into components beyond the final model.
NIST recommends documenting training-data practices where possible, addressing risks created by third-party data and software, and reevaluating models that have been fine-tuned or extended from third-party systems.
These practices resemble established software supply-chain security, but generative AI introduces additional dependencies involving models and data.
Hallucinations Are a Reliability Risk, Not Just a Content Problem
Generative AI can also produce inaccurate or fabricated information that appears credible.
OWASP includes misinformation among its current major LLM and GenAI application risks. The consequences depend heavily on how a system is used.
An inaccurate response in a brainstorming application may be relatively harmless. The same behavior becomes more serious when AI output feeds financial, security, legal, healthcare or operational decisions.
Organizations should therefore determine where human review is required and where generated information needs independent verification before an action is taken.
AI output should not become trusted merely because it is fluent or confident. Hallucinations Are a Reliability Risk, Not Just a Content Problem
Generative AI can also produce inaccurate or fabricated information that appears credible.
OWASP includes misinformation among its current major LLM and GenAI application risks. The consequences depend heavily on how a system is used.
An inaccurate response in a brainstorming application may be relatively harmless. The same behavior becomes more serious when AI output feeds financial, security, legal, healthcare or operational decisions.
Organizations should therefore determine where human review is required and where generated information needs independent verification before an action is taken.
AI output should not become trusted merely because it is fluent or confident.Hallucinations Are a Reliability Risk, Not Just a Content Problem
Generative AI can also produce inaccurate or fabricated information that appears credible.
OWASP includes misinformation among its current major LLM and GenAI application risks. The consequences depend heavily on how a system is used.
An inaccurate response in a brainstorming application may be relatively harmless. The same behavior becomes more serious when AI output feeds financial, security, legal, healthcare or operational decisions.
Organizations should therefore determine where human review is required and where generated information needs independent verification before an action is taken.
AI output should not become trusted merely because it is fluent or confident. AI chatbot safety and trust
Security Controls Need to Surround the AI System
There is no single safeguard that eliminates generative AI risk.
A stronger approach combines conventional cybersecurity controls with protections designed for probabilistic and agentic systems.
Companies should inventory where AI is being used and what data each application can reach. Access should follow least-privilege principles, particularly for systems capable of taking actions. Sensitive information should be filtered and protected, while third-party models, datasets and dependencies should be assessed as part of the technology supply chain.
Testing also needs to include AI-specific failure modes such as prompt injection, data leakage, unsafe tool use and unexpected behavior across connected applications.
Continuous logging and monitoring become particularly important for agents because organizations need visibility not only into what a model says, but also what resources it accesses and what actions it attempts.
Human approval remains appropriate for high-impact actions where an incorrect or manipulated model decision could produce substantial financial, operational, security or safety consequences.
AI Security Is Moving Beyond the Model
The broader change in 2026 is that generative AI security is becoming less about protecting an isolated chatbot and more about securing an interconnected software system.
The National Academies’ 2026 consultation on AI and cybersecurity noted that generative and agentic AI are expanding capabilities for both attackers and defenders. At the same time, recent research indicates that attack surfaces expand as systems progress from generating content to executing real-world actions.
That does not make enterprise AI inherently unsafe. It means companies need security architectures that reflect what these systems can actually do.
For organizations deploying generative AI, the most useful question is no longer simply whether a model is secure. It is what the model can access, which instructions it can trust, what actions it can take, and what happens when one of those assumptions fails.